
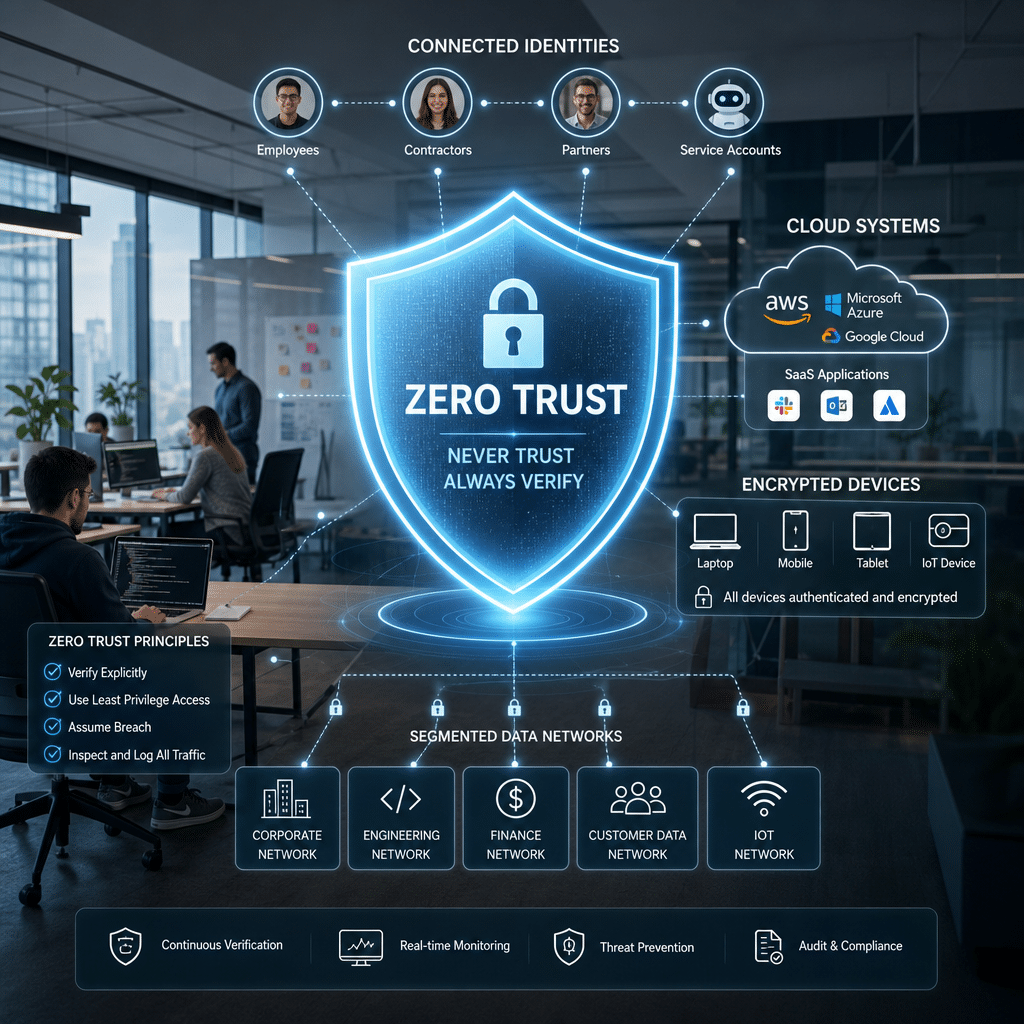
Startups move quickly, adopt new tools, and often work across offices, cloud platforms, and personal devices. That flexibility creates opportunity, but it can also make it difficult to know who has access to what, whether systems are secure, and how quickly a compromised account could spread.
A practical zero trust approach helps solve that problem without requiring an enterprise-sized security team. Instead of assuming that users, devices, or applications are safe, zero trust verifies every access request and limits permissions to what is necessary. This checklist explains how startups can build a focused, affordable security foundation that supports growth rather than slowing it down.
Table of Contents
- Understand Zero Trust Basics
- Inventory Users, Devices, and Data
- Secure Identities and Access
- Protect Devices and Endpoints
- Segment Systems and Applications
- Monitor Activity and Respond to Threats
- Build Sustainable Security Habits
- The Zero Trust Startup Checklist
- Conclusion
- Frequently Asked Questions
Understand Zero Trust Basics
Zero trust is a security model based on a simple principle: never trust automatically; always verify. Traditional security often treats users inside a corporate network as trusted. Zero trust assumes that threats can exist anywhere, including inside a network, within a cloud account, or on a legitimate employee device.
For a startup, zero trust does not mean buying every security product available. It means creating repeatable controls around identity, access, devices, applications, and data. The goal is to reduce unnecessary access and limit the damage if an account, device, or application is compromised.
What zero trust means in practice
- Verify users and devices before granting access.
- Give people only the permissions required for their roles.
- Use separate controls for sensitive applications and data.
- Continuously review access rather than approving it once and forgetting it.
- Record important security events so the team can investigate them.
Start with the systems that matter most. A focused implementation covering email, source code, cloud infrastructure, customer data, and financial systems is more valuable than a broad program that nobody can maintain.
Inventory Users, Devices, and Data
You cannot protect what you cannot see. Create a basic inventory of the people, devices, software, cloud services, and data used by the company. This list does not need to be complicated; a well-maintained spreadsheet or centralized management tool can be enough at the beginning.
Document your users
Record employees, contractors, founders, interns, and service accounts. Note each person’s team, role, manager, systems, and level of access. Include temporary accounts and accounts created by third-party vendors, since overlooked credentials are a common source of risk.
Identify critical assets
Classify your most important systems and information. Typical startup assets include customer records, payment information, intellectual property, source code, production infrastructure, employee data, and business email. Mark which systems contain sensitive data and which services can affect production or finances.
- List every cloud provider, SaaS application, and infrastructure account.
- Record system owners and backup owners.
- Identify where sensitive data is stored and shared.
- Remove unused applications and abandoned accounts.
- Review the inventory at least quarterly and whenever the company changes significantly.
Asset ownership is especially important for startups. Every critical system should have someone responsible for approving access, applying updates, and responding when something goes wrong.
Secure Identities and Access
Identity is the center of a practical zero trust program. If an attacker takes control of a valid account, network boundaries alone may not stop them. Strengthen identity controls before adding more complex security technology.
Use a central identity provider
Where possible, connect business applications to a central identity provider through single sign-on. This gives the company one place to enforce authentication policies, disable accounts, and review sign-in activity. It also reduces the number of passwords employees must manage.
Require multifactor authentication
Enable multifactor authentication for every employee and contractor, starting with administrator, email, cloud, code repository, and financial accounts. Hardware security keys or passkeys offer strong protection against phishing. Authenticator applications are also a substantial improvement over passwords alone.
Apply least privilege
Least privilege means giving each user, service, and application only the access needed to perform its job. Avoid shared administrator accounts, standing production access, and broad permissions granted for convenience. Use time-limited or approval-based access for sensitive tasks whenever possible.
- Create role-based access groups for common job functions.
- Separate development, testing, and production permissions.
- Use individual administrator accounts with strong authentication.
- Review privileged access monthly and ordinary access quarterly.
- Remove access immediately when someone leaves or changes roles.
Include an offboarding process in your checklist. On an employee’s last day, disable the identity provider account, revoke sessions and tokens, remove access to applications, rotate shared secrets if necessary, and recover company devices.
Protect Devices and Endpoints
A verified identity is not enough if the device used to access company resources is infected, outdated, or unmanaged. Establish a minimum security standard for laptops, phones, and other endpoints that connect to sensitive systems.
Define a device baseline
Require supported operating systems, automatic security updates, full-disk encryption, screen locks, and endpoint protection. Device management software can help enforce these settings, remotely lock or wipe equipment, and identify devices that fall out of compliance.
Decide whether employees may use personal devices for business access. If they can, limit the data those devices can download and use separate work profiles or mobile management controls. A clear policy is safer than an informal exception that nobody monitors.
- Maintain an approved device list.
- Install endpoint detection or reputable anti-malware protection.
- Block local administrator rights for routine work where practical.
- Require automatic screen locking and encrypted storage.
- Provide a process for reporting lost or stolen devices.
Do not overlook developer workstations and cloud administration devices. These endpoints often hold credentials, code, tokens, or access to production environments and deserve stronger controls than ordinary browsing devices.
Segment Systems and Applications
Zero trust reduces the assumption that access to one resource should lead to access to everything else. Segmentation helps contain incidents by separating users, applications, environments, and data according to business need.
Separate environments
Keep development, staging, and production environments distinct. Use different credentials and service accounts, restrict production access, and avoid copying real customer data into development unless it has been properly anonymized. This limits the impact of a compromised developer account or test system.
Control application connections
Review integrations between SaaS tools, APIs, databases, and cloud services. Remove unused integrations and restrict tokens to specific actions and resources. Set expiration dates for credentials where the platform supports them, and store secrets in a dedicated secrets manager rather than in code or shared documents.
Network segmentation can be valuable, but startups should think beyond network location. Application-level permissions, API authorization, cloud policies, and database controls are often more useful than relying on a single corporate VPN. Ask whether each connection is necessary, authenticated, authorized, and logged.
Monitor Activity and Respond to Threats
Zero trust is not a one-time configuration. Monitoring helps you confirm that controls work and identify suspicious activity before it becomes a serious incident.
Collect useful security signals
At a minimum, collect authentication events, administrator actions, access to sensitive data, changes to cloud infrastructure, and endpoint alerts. Centralize these logs when possible and protect them from unauthorized modification. You do not need to analyze every event manually, but you should know which alerts require immediate attention.
- Alert on impossible-travel or unusual sign-ins.
- Monitor repeated failed authentication attempts.
- Review new administrator privileges and access policy changes.
- Track unusual downloads, data transfers, or API activity.
- Notify the team when security tools or logs are disabled.
Create an incident response plan
Write down what happens if an account is compromised, a laptop is lost, or customer data is exposed. Assign decision-makers, technical responders, communications owners, and legal or compliance contacts. Include vendor contact details and instructions for preserving evidence.
Run a short tabletop exercise at least once a year. Discuss how the team would isolate a device, revoke credentials, communicate with customers, restore systems, and learn what happened. Practicing before an incident reduces confusion when time matters.
Build Sustainable Security Habits
Technology cannot compensate for unclear ownership or inconsistent behavior. Make security part of normal startup operations through concise policies, onboarding, training, and regular reviews.
Train people for realistic threats
Teach employees how to recognize phishing, malicious links, fake support requests, credential theft, and social engineering. Explain how to report suspicious messages without blame. Training should be relevant to each role, especially for finance, engineering, customer support, and leadership.
Manage vendors and changes
Before adopting a new service, ask what data it handles, how it authenticates users, where information is stored, and how access can be revoked. Limit vendor permissions and review them periodically. Include security requirements in contracts when the vendor processes sensitive or regulated data.
Use a lightweight change process for production systems and security settings. Record what changed, who approved it, and how to reverse it. This creates accountability without imposing heavy bureaucracy on a small team.
The Zero Trust Startup Checklist
Use the following checklist as a practical starting point. Prioritize the controls that protect your most valuable assets and address the most likely threats.
- Map the environment: inventory users, devices, applications, cloud accounts, data, integrations, and service accounts.
- Centralize identity: connect important applications to a trusted identity provider and eliminate unnecessary local accounts.
- Turn on MFA: require phishing-resistant authentication for privileged users and MFA for everyone else.
- Apply least privilege: define role-based access, remove shared administrator accounts, and make production access temporary where possible.
- Automate joiner and leaver processes: provision and revoke access quickly when people join, leave, or change roles.
- Set device requirements: enforce encryption, updates, screen locks, endpoint protection, and remote-wipe capabilities.
- Separate environments: isolate production from development and protect secrets, tokens, and service accounts.
- Secure data: classify sensitive information, limit sharing, encrypt it in transit and at rest, and define retention rules.
- Monitor important events: collect authentication, administrative, cloud, endpoint, and data-access logs.
- Prepare for incidents: document response steps, assign owners, maintain contacts, and test the plan.
- Review regularly: reassess access, vendors, devices, policies, and risks at least quarterly.
Track progress using a small set of measurable goals, such as MFA coverage, percentage of managed devices, number of stale accounts, time to revoke leaver access, and completion of access reviews. These metrics help founders and teams see whether the program is improving.
Conclusion
A startup does not need an enormous security budget to adopt zero trust. It needs visibility, strong identity controls, carefully limited access, secure devices, separated systems, useful monitoring, and a response plan that people understand.
Begin with the accounts and assets that could cause the greatest harm if compromised. Then improve the controls in manageable stages, assign clear owners, and review the program as the company grows. A practical zero trust checklist turns security from a vague objective into a repeatable operating habit.
Frequently Asked Questions
What is zero trust in simple terms?
Zero trust means no user, device, application, or network location is trusted automatically. Every access request is verified, authorized, and limited to the resources required.
Can a small startup implement zero trust without a security team?
Yes. Start with an identity provider, multifactor authentication, least-privilege access, managed devices, basic logging, and a documented incident response plan. These controls provide meaningful protection without requiring a large team.
What should a startup prioritize first?
Prioritize email and administrator account security, MFA, employee onboarding and offboarding, device encryption and updates, access reviews, and protection for production infrastructure and customer data.
How often should zero trust controls be reviewed?
Review privileged access monthly and broader user, device, vendor, and application access at least quarterly. Reassess immediately after a role change, acquisition, major product launch, or security incident.
Leave a Reply